PHP releases security updates after vulnerabilities put websites at risk
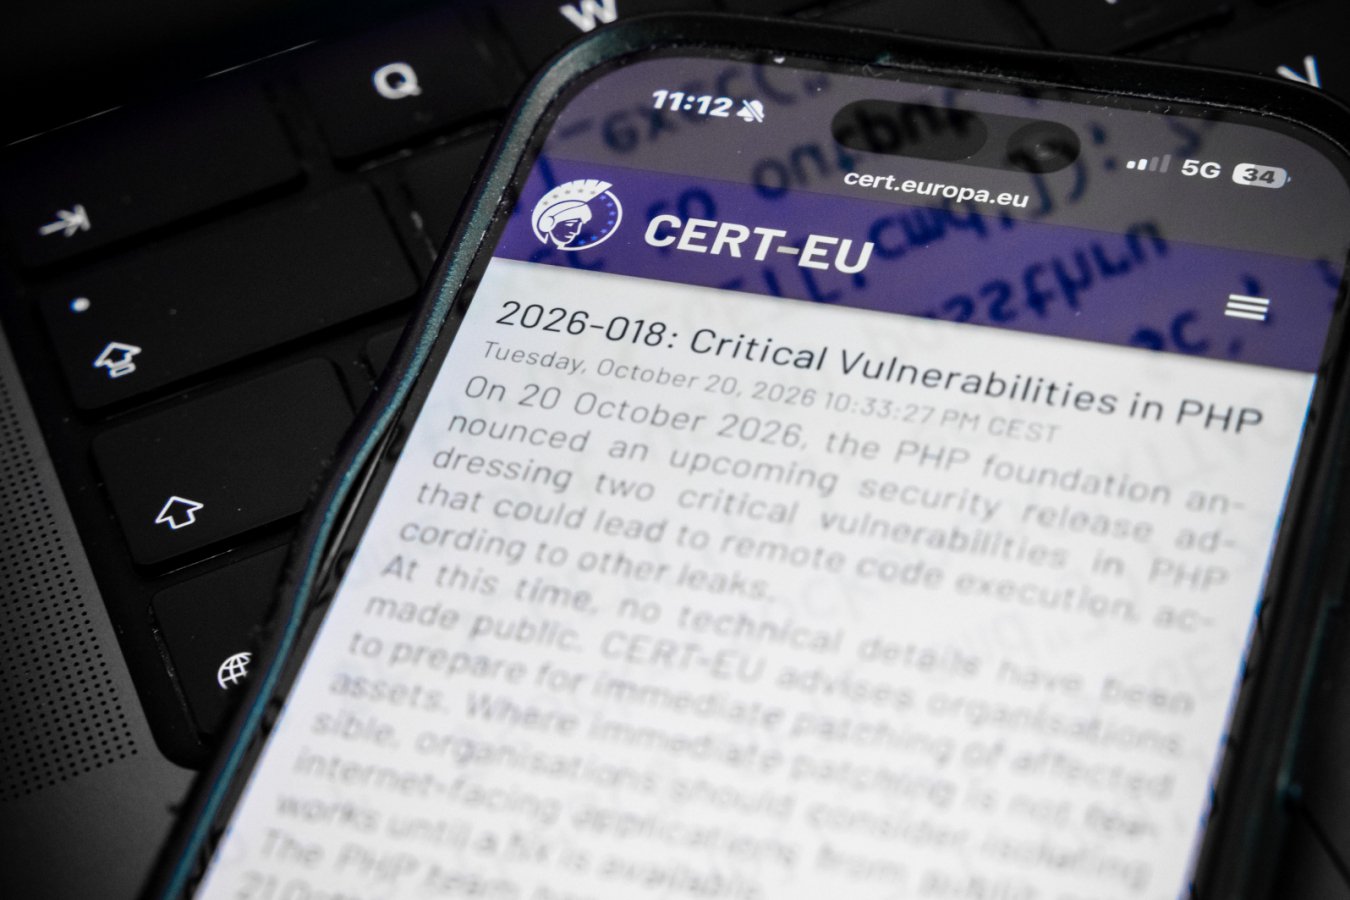
The PHP project released four updated versions after researchers found vulnerabilities that could expose data or let attackers run code on servers. The PHP Foundation urged PHP users to update immediately.
Key takeaways · 4
- 01
The PHP project released versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35; the PHP Foundation urged users to update immediately.
- 02
The vulnerabilities could allow unauthenticated attackers to execute code on PHP servers.
- 03
The reported exposure concerns websites, not individuals’ personal computers.
- 04
The PHP Foundation said fixes were difficult because the affected functions are central to PHP and changes could bring compatibility or performance costs.
What PHP announced
The PHP project released PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.[1] The PHP Foundation said vulnerabilities could let an unauthenticated attacker execute code on servers running PHP.[1] It also said errors can leave data behind that a malicious actor may access, including private information, or use to run malicious code.[2] Remote code execution was confirmed on PHP-FPM through application-level code paths, the Foundation said.[1] The Foundation urged PHP users to update immediately.[1]
Who may be affected
New Scientist reported that about 70 per cent of websites worldwide were vulnerable to data theft and defacement because of the flaw.[2] It said PHP is commonly used to power websites and services including WordPress, Facebook and Wikipedia.[2] The vulnerability affects websites rather than individuals’ personal computers.[2] Every PHP version released in the decade before the report was affected by at least one of the vulnerabilities.[2] For teams assessing exposure, the reported scope makes it important to check the PHP versions used on their web servers rather than treating this as a desktop-computer update.[2]
Why the fix was difficult
The PHP Foundation said the vulnerabilities affected central PHP functions, making them difficult to fix without potential compatibility or performance costs.[1] A PHP core developer found the first signs of the out-of-memory problem while fixing an issue reported by Quarkslab.[1] The Foundation said a potential exploit had been theorized in 2024, but researchers had not found concrete attack vectors at that point.[1] It attributed the delay in fixing the issue to a flawed decision process and insufficient resources.[1] These details indicate why updating is the immediate action available to PHP users, even as the underlying fixes carry trade-offs.[1]
Exploitation and response
Cloudflare counted thousands of exploits in the hours before the announcement, after an apparent leak of vulnerability information, RNZ reported.[3] Separately, the PHP Foundation said its security team had not identified functional exploits at the time of release or public disclosure.[1] Alan Woodward of the University of Surrey said exploitation requires millisecond timing, but many attempts could be run until one finds the right answer.[2] New Scientist reported that government websites in France, Denmark, Finland and the Netherlands were taken offline as a precaution.[2] Woodward said smaller websites with fewer resources could remain vulnerable for months or years.[2]
Professionals responsible for websites should use the release as a prompt to identify PHP deployments and plan updates, weighing compatibility and performance considerations. Smaller teams may need to pay particular attention to whether they can complete that work promptly.
Why it matters
Bring this to your team — one session a day, built for your industry.
kju.ai is built for teams: daily sessions, team analytics, and rollout support for your organization.
For teamsHow this developed
24 October 2026
PHP releases security updates after vulnerabilities put websites at risk
Sources
- Today's PHP Security Release, and How We're Strengthening PHP Security — The PHP Foundation — Supporting, Advancing, and Developing the PHP Languagethephp.foundation
- Global race to update computers as AI discovers most disruptive hack yet | New Scientistnewscientist.com
- The biggest internet security threat has been known for 22 years. AI made it a crisis in two days | RNZrnz.co.nz