OpenAI reports 948 Linux kernel privilege-escalation vulnerabilities
OpenAI says a pipeline powered by an upcoming cyber model identified 948 distinct Linux kernel local privilege-escalation vulnerabilities after variant analysis. The company says an unprivileged local user could use the exploits to gain root access.
Key takeaways · 4
- 01
OpenAI says the pipeline produced 948 distinct patches, which it counts as unique local privilege-escalation vulnerabilities.
- 02
The reported figures distinguish 1,169 working exploits from 948 unique vulnerabilities after variant analysis.
- 03
OpenAI says human researchers review exploits, patches and proposed severity before vulnerabilities are reported to maintainers.
- 04
The full research run cost $1,213,430 in API credits; OpenAI says cost was not the study’s focus.
How the pipeline worked
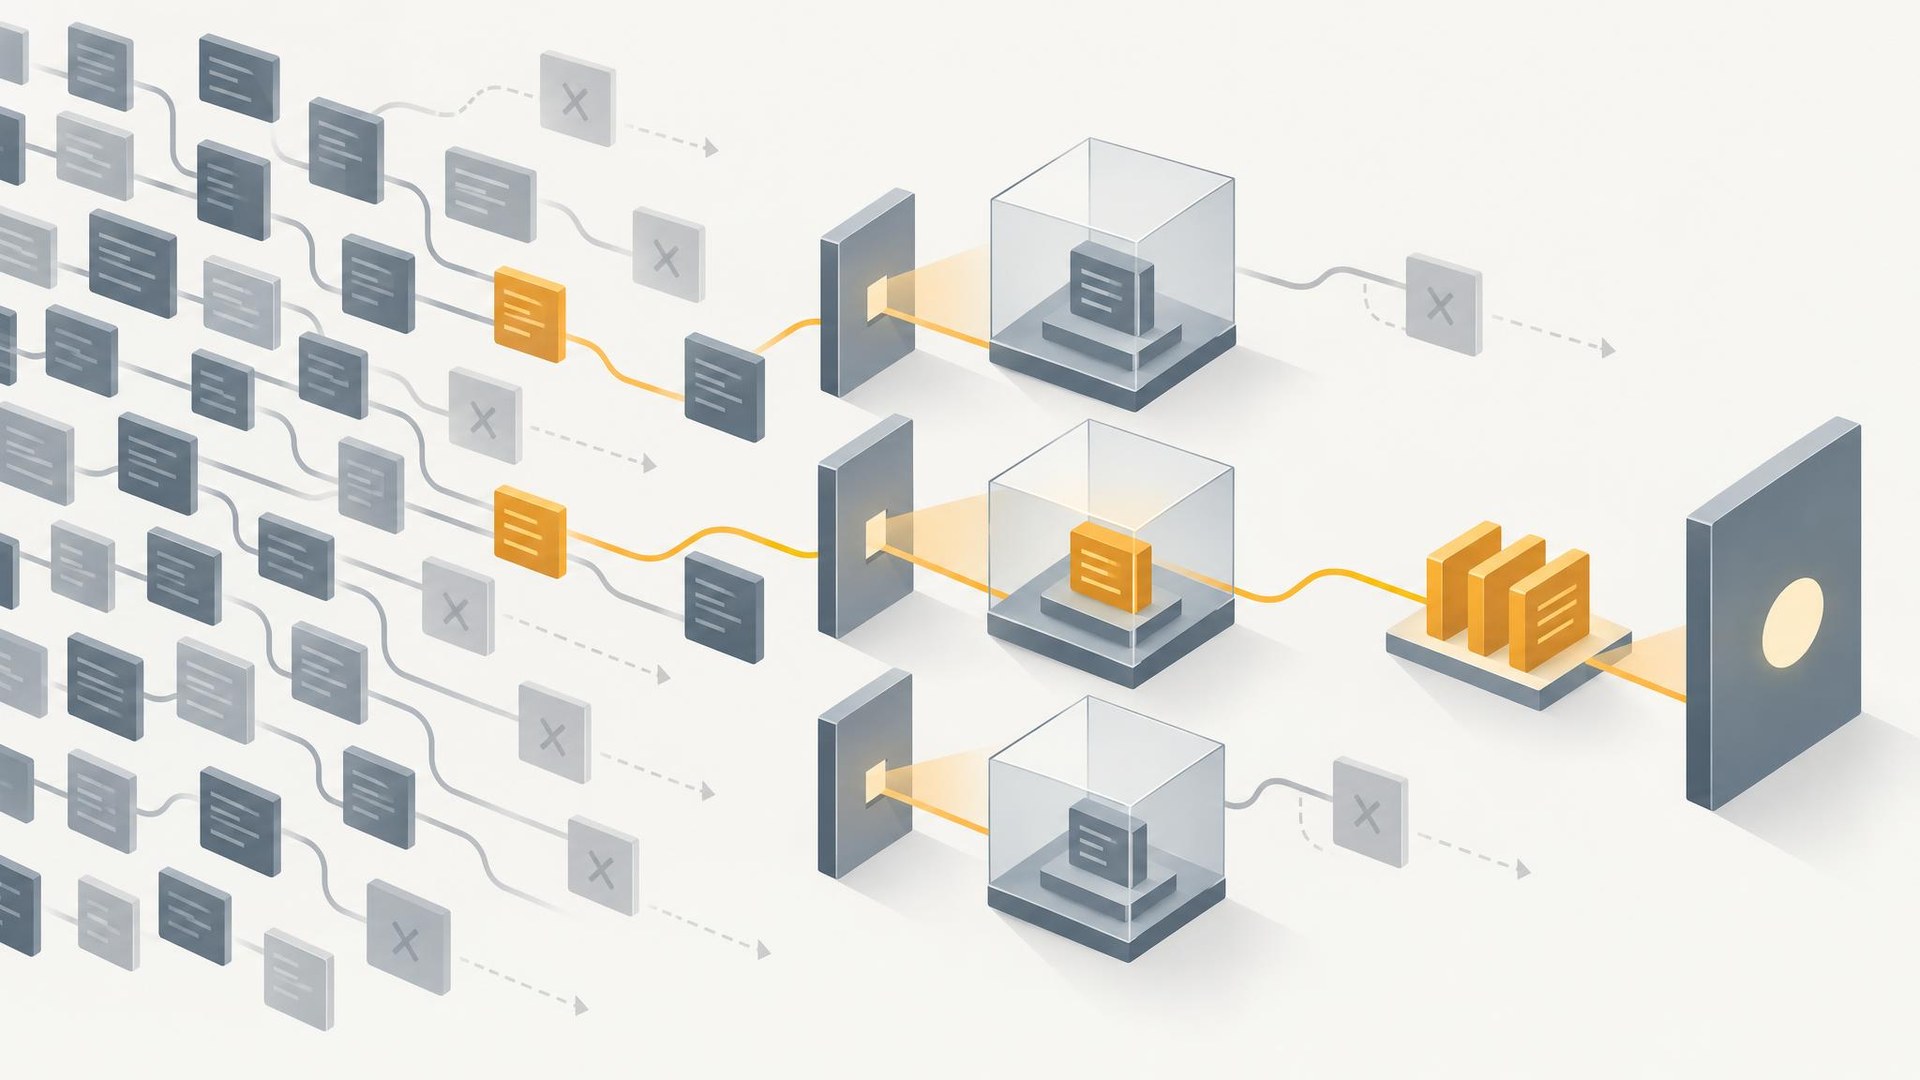
OpenAI describes a pipeline that identifies security-relevant Linux kernel code, statically scans audit targets and dynamically reproduces findings in an isolated environment.[1] Scout agents selected targets based on whether low-privileged users could reach the code and on its security relevance.[1] The Scouts selected 5,034 targets covering about 2.8 million lines of code, roughly 7% of the kernel, according to OpenAI.[1] OpenAI says the target virtual machines ran a stock desktop operating system, rather than a weakened target.[1] The Linux kernel contains more than 40 million lines of code, OpenAI notes.[1]
What the reported numbers mean
OpenAI says Analyst agents produced 2,308 deduplicated candidate findings within 12 hours; the pipeline reproduced 1,724 vulnerabilities.[1] Its reported total of 948 is not the same as its exploit count: OpenAI says exploit-development agents produced 1,169 working local privilege-escalation exploits, then variant analysis yielded 948 distinct patches, which it counts as unique vulnerabilities.[1] OpenAI also says 3.1% of candidate findings reflected incorrect model analysis because they relied on an impossible condition.[1] The output for a finding can include root-cause analysis, a minimal crashing proof of concept, a candidate patch and a full exploit.[1]
Review and disclosure
OpenAI says human researchers review the exploit, patch and proposed severity before reporting vulnerabilities to maintainers.[1] It says it began with critical vulnerabilities, following Linux kernel community guidance, and is working with Patch the Planet partners on additional reports and patches.[1] OpenAI reports that the mid-October run found more than five times as many novel local privilege-escalation vulnerabilities as a July GPT-5.6 Sol run, despite three months of kernel hardening.[1] The company says it knows of at least 10 novel Linux exploitation techniques discovered and used by the agents; Unite.AI reports that OpenAI withheld full technical details for safety reasons.[1][2]
Cost and earlier results
OpenAI reports that the full research run cost $1,213,430 in API credits, or about $1,279 per local privilege-escalation exploit.[1] It says the research focused on methodology and measuring model capability, not cost.[1] In an earlier run, OpenAI found that 20 of 200 reported successful exploits reached root through a different zero-day than the assigned vulnerability.[2] That earlier result is a separate caveat, not a reported rate for the mid-October run.[2][1] OpenAI also says its June work with GPT-5.5 Cyber identified kernel vulnerabilities and developed 24 local privilege-escalation exploits.[1]
The results suggest AI-assisted vulnerability discovery can generate findings and working exploits at a scale that makes validation and coordinated disclosure central parts of the workflow. For teams assessing similar tools, the distinction between candidate findings, reproduced vulnerabilities, exploits and unique vulnerabilities matters when estimating review effort or security impact.
Why it matters
Bring this to your team — one session a day, built for your industry.
kju.ai is built for teams: daily sessions, team analytics, and rollout support for your organization.
For teamsHow this developed
5 November 2026
OpenAI reports 948 Linux kernel privilege-escalation vulnerabilities